Duplicates Are Part Of The Process
A duplicate is not a rejection. It is the one closure reason that confirms you found a real, in-scope, payable bug. Here is what to do when they stack up.
I'm Amr Elsagaei, also known as AmrSec. I'm a security researcher, bug bounty hunter and developer.
I report vulnerabilities to some of the world's largest companies and work with their security teams to get them fixed.
On YouTube and here I break down what I find: the bugs, the tools and the process, so other hunters can use it.
Security vulnerabilities found and reported to the teams who own the systems, across companies of every size.
and 100+ more
A duplicate is not a rejection. It is the one closure reason that confirms you found a real, in-scope, payable bug. Here is what to do when they stack up.
Cache poisoning tests aim at the edge because only the edge answers back. The inner caches behind one response, and why a cache buster buys nothing.
DOM clobbering turns named element references into overwritten globals, so HTML injection with no XSS is not a dead end. The bundler chains it breaks.
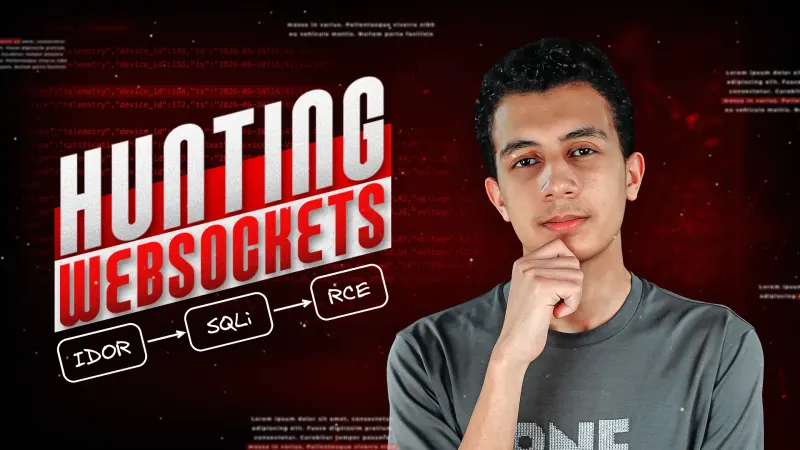
Most hunters close the tab at 101 Switching Protocols. A five-step WebSocket recipe, from broken authorization and IDOR to cross-site hijacking.
Authentication for bug bounty hunters: sessions, cookie flags, JWTs, OAuth 2.0, OIDC and PKCE, and the auth gaps that lead to account takeover.
A report generator missing ownership checks, CSS injection through a live cursor, and a Python sandbox that wasn't one. All found in the final hour.
Walkthroughs, tooling and live hunting from the channel.
Views32DurationPublished
Views5.7KDurationPublished
Views1.1KDurationPublished
Views3.7KDurationPublished
Views8.8KDurationPublished
Views4.6KDurationPublished
Views13KDurationPublished
Views1.1KDurationPublished
Views6.1KDurationPublished
Partners
I work with companies around the world on security research, bug bounty and collaborations.